What is a DDoS attack and how do you protect your website against it?
Your website is suddenly inaccessible, for no apparent reason. No error message in your CMS, no problem with your hosting provider, just... nothing. This is one of the most common symptoms of a DDoS attack. In this article, we explain what it is, how it works, and how to protect your website against it.
What is a DDoS attack?
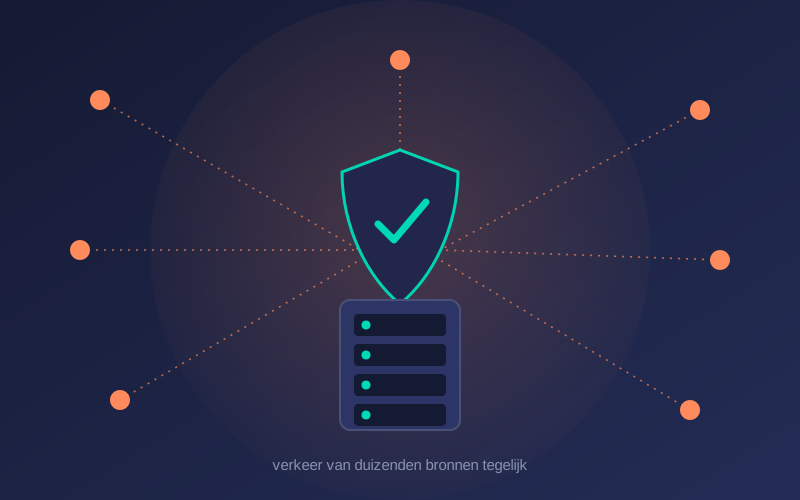
DDoS stands for Distributed Denial of Service. In such an attack, a website or server is flooded with an enormous amount of traffic originating from countless different sources simultaneously. The goal is not to steal data, but to overload the website or server, rendering it inaccessible to ordinary visitors.
The word "distributed" refers to the fact that the attack does not originate from a single source, but from thousands or even millions of devices simultaneously, often without the knowledge of the owners of those devices. These networks of hijacked devices are called botnets.
How does a DDoS attack work?
A server can only process a limited number of requests at a time. In a DDoS attack, that limit is deliberately exceeded by sending so many requests simultaneously that the server, network, or website application can no longer handle it. As a result, legitimate visitors experience slow loading times or error messages, or the website is completely inaccessible.
There are different types of DDoS attacks, targeting different layers of a website: some simply overwhelm the network connection, while others specifically target weak points in a website application.
Why do websites become the target of DDoS?
Competition or sabotage : sometimes a DDoS attack is intended to temporarily disable a competitor.
Extortion : attackers sometimes threaten a DDoS attack unless a ransom is paid.
Activism or protest : certain groups use DDoS attacks to draw attention to a point of view.
Diversion : a DDoS attack can also be used as a diversionary tactic, while another attack takes place in the background.
What are the consequences of a DDoS attack?
Loss of revenue , especially for webshops that cannot process orders during the attack.
Reputational damage , because visitors perceive your website as unreliable.
Additional costs , for example due to extra server usage during the attack.
Reduced customer trust, especially in the case of repeated incidents.
How do you protect your website against DDoS attacks?
Server-level DDoS protection. A good hosting provider offers active DDoS protection that recognizes and filters suspicious traffic before it reaches your website.
Content Delivery Network (CDN) A CDN distributes your website across multiple servers worldwide, making it easier to handle sudden traffic spikes.
Rate limiting By limiting the number of requests a single visitor is allowed to make within a certain time, it becomes more difficult to overwhelm a server.
Monitoring Continuous monitoring of your server traffic makes it possible to quickly detect unusual spikes and take action.
An emergency plan. Know in advance who to contact and what steps to take if your website does become a target. Time is crucial during an attack.
What can't you do yourself against DDoS?
DDoS protection requires specialized infrastructure that goes beyond what an individual website owner can set up themselves. It is therefore primarily the responsibility of your hosting provider to provide this protection by default, especially for business-critical websites.
Conclusion
A DDoS attack can affect any website, regardless of size or sector. The best protection combines active monitoring, specialized infrastructure, and a hosting provider that is equipped for this as standard. At Mediawax, DDoS protection is included as standard in our hosting packages, so you don't have to worry about unexpected downtime.


